Onboard an On-Premises Firewall Management Center to Security Cloud Control Firewall Management
Onboarding an On-Premises Firewall Management Center to Security Cloud Control Firewall Management is an integration process that
-
enables centralized device visibility and management across security infrastructure
-
provides consistent policy enforcement through shared object management, and
-
supports zero-touch provisioning of devices and cloud assist capabilities.
Onboarding methods and capabilities
Security Cloud Control Firewall Management provides two methods to onboard On-Premises Firewall Management Centers.
-
Use On-Premises Firewall Management Center credentials with SDC is supported but intended only for very rare use cases. Onboarding with SDC limits access to many cloud assist features available with direct onboarding. Choose SDC if direct onboarding is not possible.
Security Cloud Control complements FMC by enabling:
-
Consistent policy enforcement through shared object management with FMCs.
-
Zero-touch provisioning of Firewall Threat Defense devices. For more information, refer to Onboard a Device to On-Premises Firewall Management Center with Zero-Touch Provisioning.
-
Centralized visibility and management of security devices. For more information, refer to Device and Service Management.
-
Integration with cloud Cisco Secure Dynamic Attributes Connector (CSDC) and Cloud-Delivered Firewall Management Center. For more information, refer to Cisco Secure Dynamic Attributes Connector.
Configuration limitations and guidelines:
-
Onboarding an On-Premises Firewall Management Center also onboards all devices registered to it. Disabled or unreachable devices may appear in the Security Devices page in Security Cloud Control but cannot be managed or queried.
-
Onboarding does not cascade policies from On-Premises Firewall Management Center to Security Cloud Control or Cloud-Delivered Firewall Management Center. To migrate Firewall Threat Defense devices to Cloud-Delivered Firewall Management Center, use the built-in Migrate FTD to Cloud-Delivered Firewall Management Center feature. For more information, refer to Migrate Threat Defense to Cloud-delivered Firewall Management Center.
-
We recommend creating a dedicated user on the On-Premises Firewall Management Center with administrator-level permissions specifically for Security Cloud Control communication. If you log in to On-Premises Firewall Management Center with the same credentials during onboarding, the process will fail. This recommendation applies only to credentials-based onboarding, not to direct integration.
-
For this dedicated user, set the Maximum Number of Failed Logins to zero.
-
For On-Premises Firewall Management Centers version 7.4 or later, if a switchover causes a loss of cloud connectivity, disable and then re-enable SecureX, Security Cloud Control, or Cisco Security Cloud (depending on your version) to restore the connection.
Onboard an On-Premises Firewall Management Center to Security Cloud Control with Credentials
This task enables centralized management of your On-Premises Firewall Management Center through Security Cloud Control by establishing secure connectivity and authentication.
To onboard an On-Premises Firewall Management Center to Security Cloud Control with credentials, follow this procedure:
Before you begin
These prerequisites must be met:
-
For Cloud Secure Device Connector (SDC): Allow inbound traffic on port 443 of the On-Premises Firewall Management Center.
The SDC reaches the On-Premises Firewall Management Center by allowing inbound traffic on port 443.
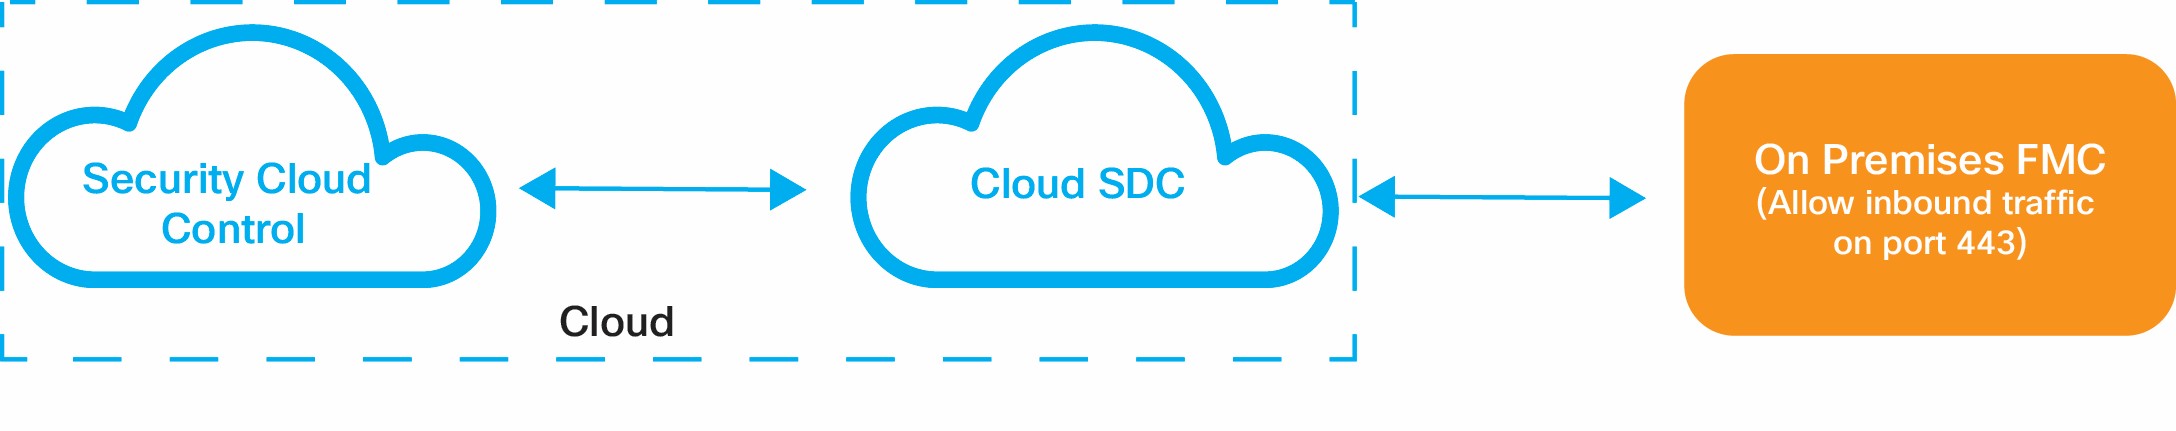
Both the Security Cloud Control and the SDC are hosted in the cloud.
-
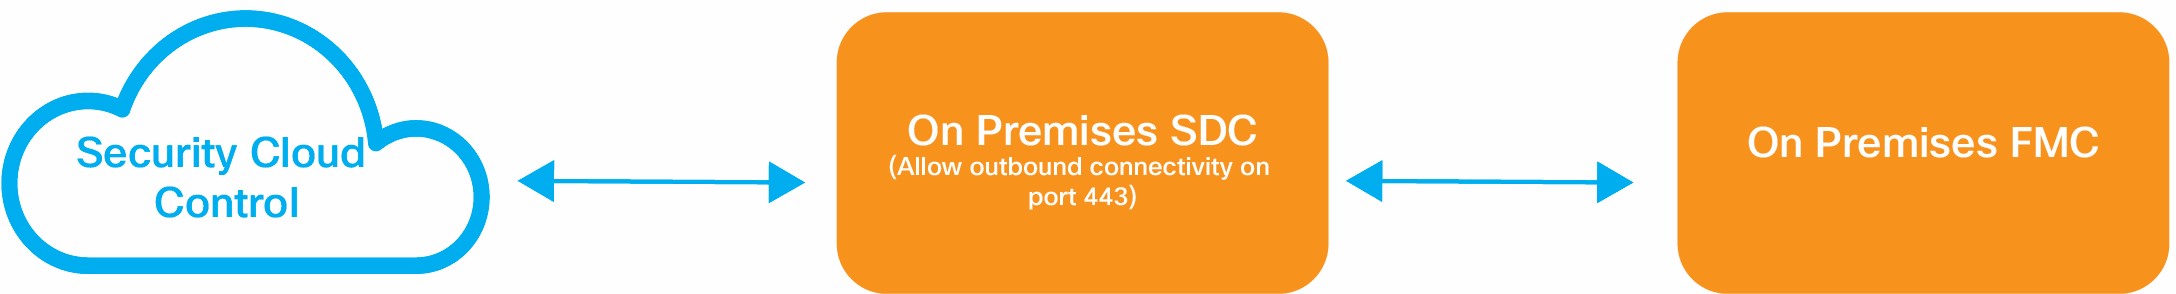
For On-Premises Secure Device Connector (SDC): Allow outbound connectivity on port 443 of the SDC.
The SDC requires connectivity to the Security Cloud Control, making it imperative to permit outbound traffic from the SDC to the Security Cloud Control. No additional port configuration is required on on-premises Firewall Management Center.
Procedure
|
Step 1 |
Choose . |
||
|
Step 2 |
Choose . |
||
|
Step 3 |
Click |
||
|
Step 4 |
Click Firewall Management Center. |
||
|
Step 5 |
Select the Use Credentials card. |
||
|
Step 6 |
Enter the device name and location and click Next. |
||
|
Step 7 |
Enter the Username and Password of the account credentials you want to use to access the On-Premises Firewall Management Center. Click Next. |
||
|
Step 8 |
After you onboard the device, you can add labels to your On-Premises Firewall Management Center, or you can click Go to Services to view the page of onboarded devices. If the device is healthy, the FMC displays a Synced status.
|
 to onboard an

The On-Premises Firewall Management Center is successfully onboarded to Security Cloud Control and can be managed centrally with a Synced status indicating successful connectivity.
Redirect Security Cloud Control to an On-Premises Firewall Management Center
Update the management interface hostname to enable cross-launch functionality from Security Cloud Control to the On-Premises Firewall Management Center UI.
After you onboard an On-Premises Firewall Management Center to Security Cloud Control, update the management interface's hostname in the On-Premises Firewall Management Center UI so that it contains the FQDN. If you do not update the management interface's hostname, you cannot cross-launch from Security Cloud Control.
Follow these steps to update the management interface hostname and redirect from Security Cloud Control to On-Premises Firewall Management Center:
Procedure
|
Step 1 |
Log in to the On-Premises Firewall Management Center UI. |
||
|
Step 2 |
Choose . |
||
|
Step 3 |
Click the Management Interfaces tab. |
||
|
Step 4 |
Under Shared Settings, locate the Hostname field and enter the Firewall Management Center's FQDN. |
||
|
Step 5 |
Click Save.
|
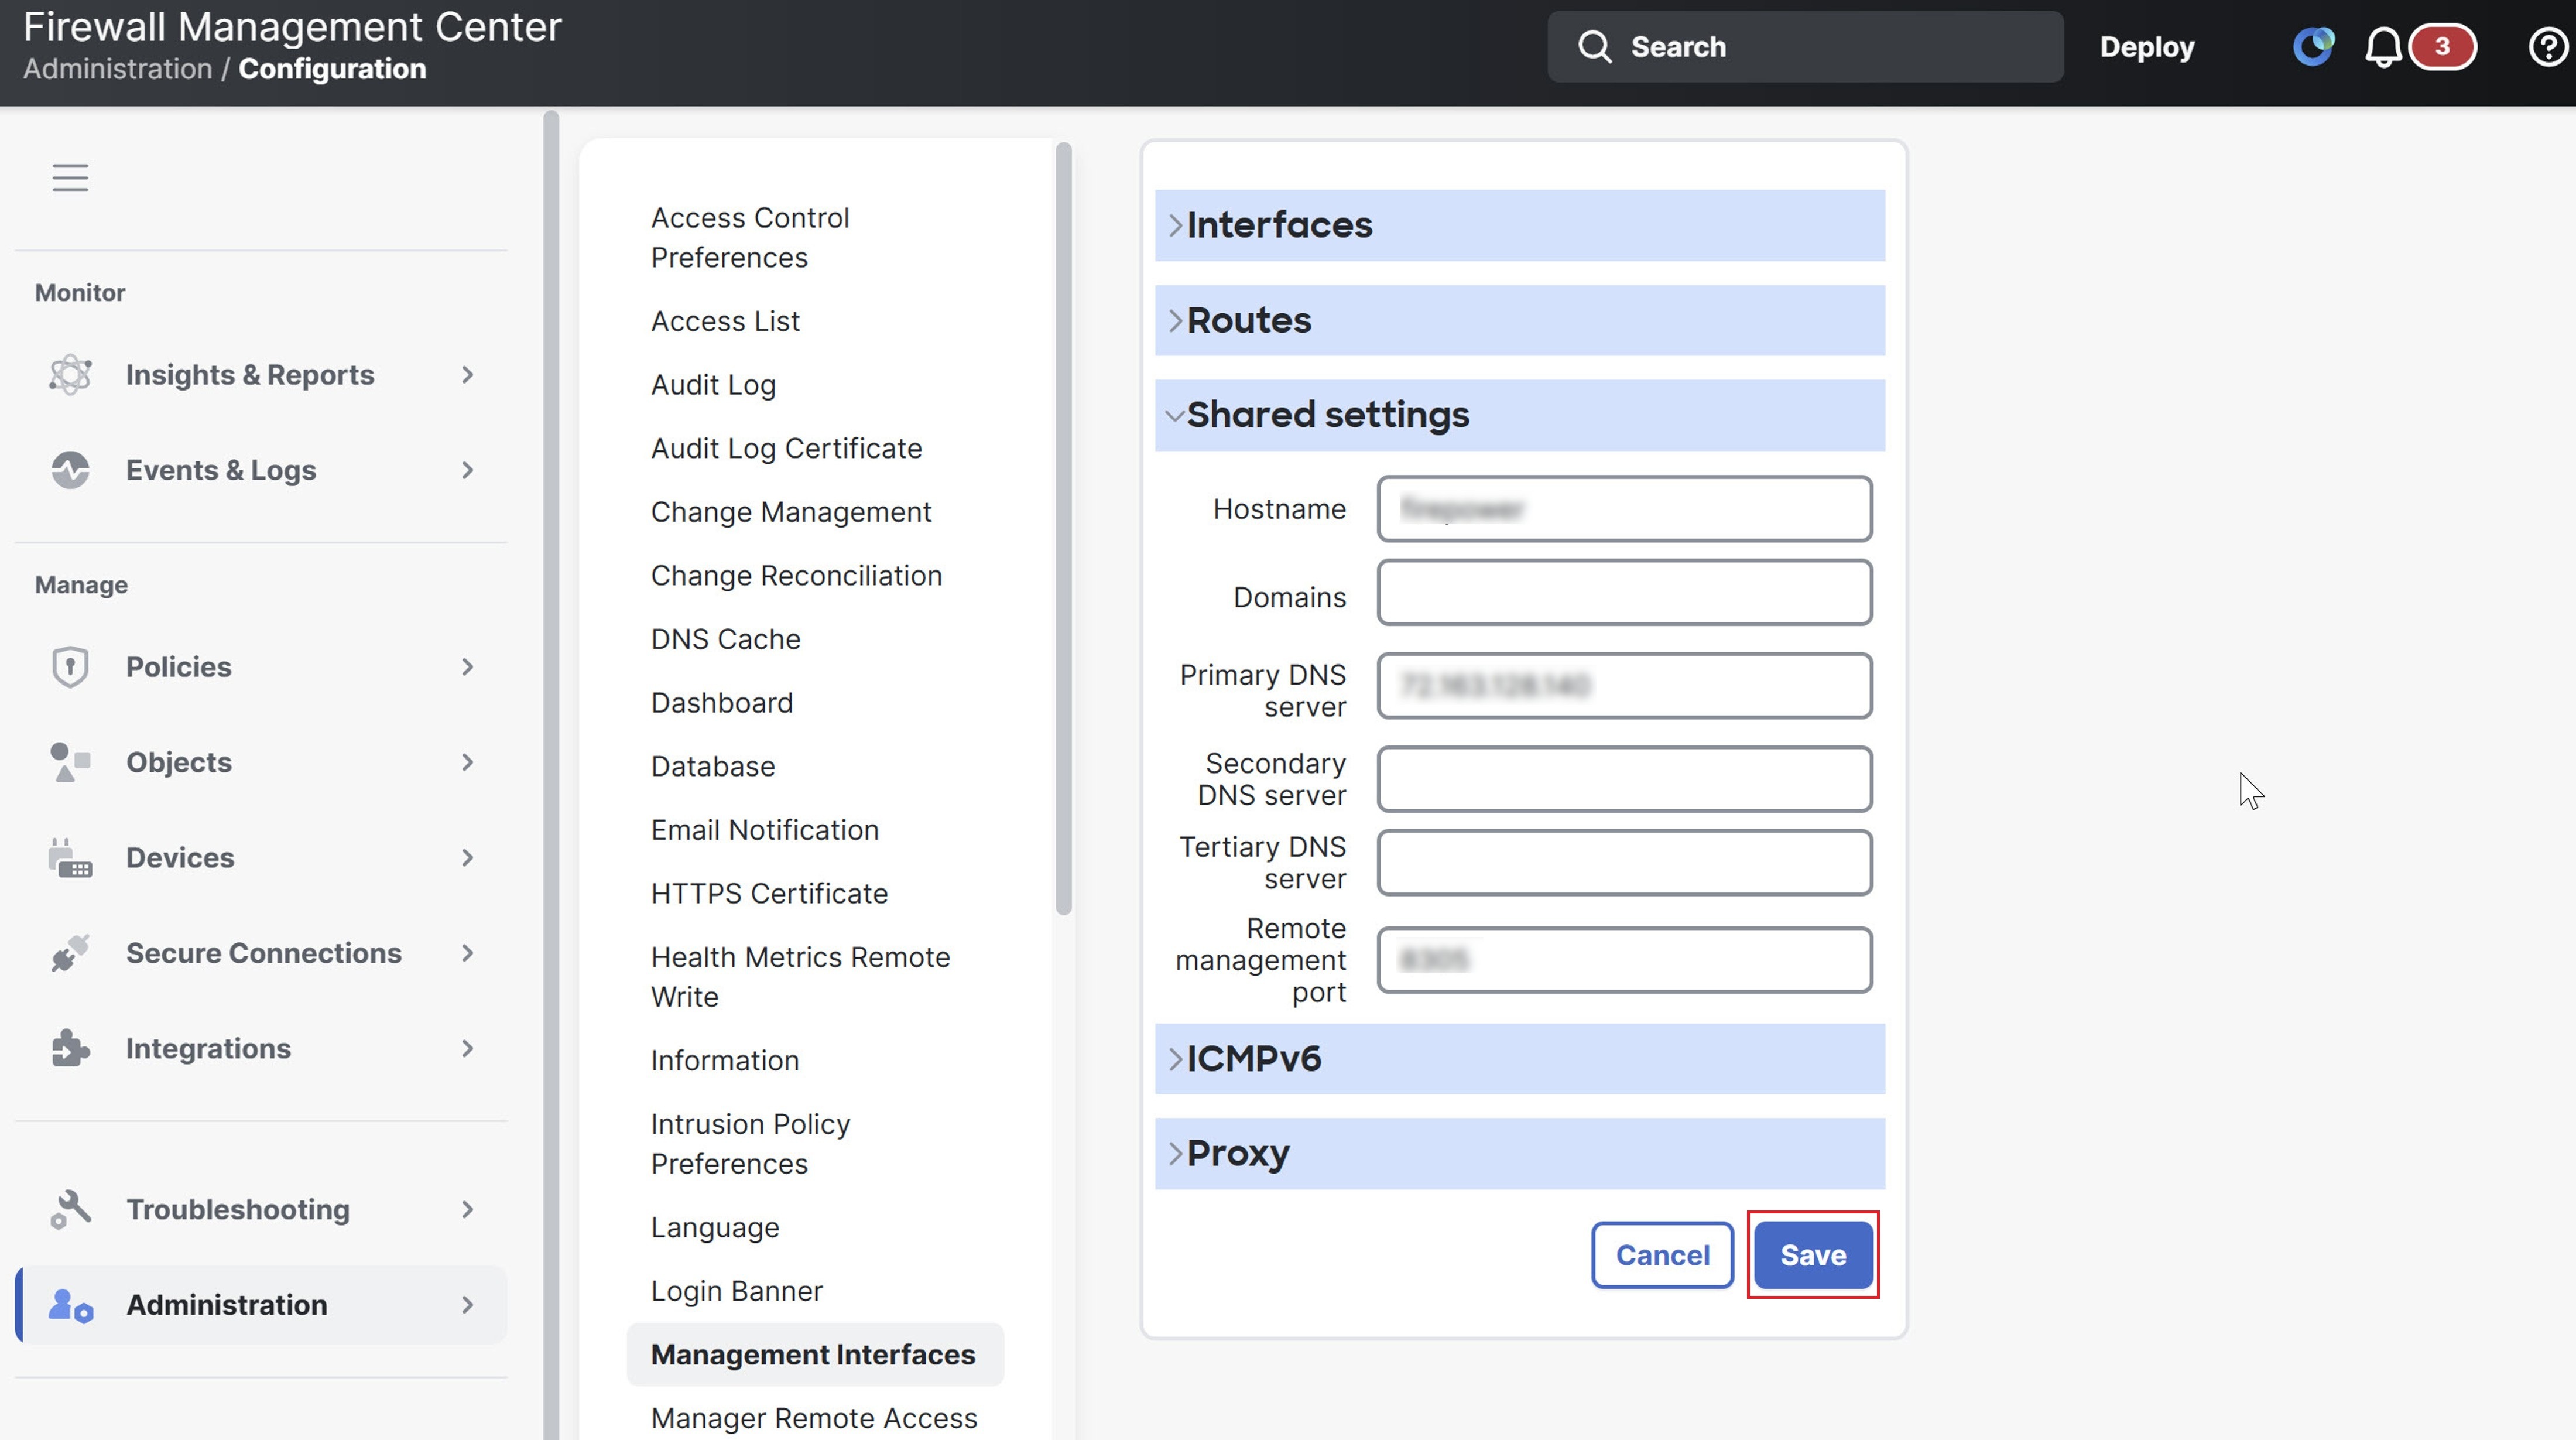
The management interface hostname is updated with the FQDN, enabling cross-launch functionality from Security Cloud Control to the On-Premises Firewall Management Center UI.
 Feedback
