Manage onboarded device settings

This chapter provides guidance on managing the device settings of the onboarded device.

Change a device's IP address in Security Cloud Control Firewall Management

Update the IP address stored in Security Cloud Control Firewall Management to match a device's new IP address without changing the device's configuration.

When you onboard an device to Security Cloud Control Firewall Management using an IP address, Security Cloud Control Firewall Management stores that IP address in its database and communicates with the device using that IP address. If the IP address of the device changes, you can update the IP address stored in Security Cloud Control Firewall Management to match the new address. Changing the device's IP address on Security Cloud Control Firewall Management does not change device's configuration.

To change the IP address, Security Cloud Control uses to communicate with a device, follow this procedure:

Procedure


Step 1

Choose Inventory.

Step 2

Choose Security Devices

Step 3

Click the Devices tab to locate the device.

Step 4

Click the appropriate device type tab.

You can use the filter and search functionalities to find the required device.

Step 5

Select the device whose IP address it is you want to change.

Step 6

Above the Device Details pane, click the edit button next to the device's IP address.
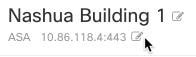
The image illustrates the process of changing a device's IP address, highlighting the relevant interface and options available in the configuration settings.

Step 7

Enter the new IP address in the field and click the blue check button.

No change is made to the device itself, so the device's Configuration Status will continue to show that it is Synced.


The IP address stored in Security Cloud Control Firewall Management is updated to the new address, and Security Cloud Control will communicate with the device using the new IP address.
Change a device's name in Security Cloud Control Firewall Management

Change device names to improve organization and identification in your inventory without affecting the actual device configuration.

All devices, models, templates, and services are given a name when they are onboarded or created in Security Cloud Control Firewall Management. You can change that name without changing the configuration of the device itself.

Procedure


Step 1

Choose Inventory.

Step 2

Choose Security Devices.

Step 3

Click the Device tab to locate the device.

Step 4

Select the device whose name it is you want to change.

Step 5

Above the Device Details pane, click the edit button next to the device's name.

The device's name is updated in the inventory while its Configuration Status remains Synced, indicating no changes to the device itself.

Step 6

Enter the new name in the field and click the blue check button.

No change is made to the device itself, so the device's Configuration Status will continue to show that it is Synced.


The device appears with its new name in your inventory, while maintaining its synchronized configuration status.

Export a list of devices and services

Export your list of devices and services to a comma-separated value (.CSV) file that can be opened in spreadsheet applications for sorting and filtering.

This article explains how to export your list of devices and services to a comma-separated value (.CSV) file. Once in that format, you can open the file in a spreadsheet application such as Microsoft Excel to sort and filter the items in your list.

The export button is available in both the Devices and Templates tab. You can also export details from devices under the selected device type tab.

Before you export your list of devices and services, look at the filter pane and determine if the Security Devices page is displaying the information you want to export. Clear all filters to view all managed devices and services, or apply filters to display a subset of your devices and services. The export function includes only the information currently displayed in the Security Devices page.

Procedure


Step 1

Choose Inventory.

Step 2

Choose Security Devices.

Step 3

Click the Devices tab to locate the device or the Templates tab to locate the model device.

Step 4

Click the appropriate device type tab to export details from devices under that tab or click All to export details from all devices.

You can use the filter and search functionalities to find the required device.

Step 5

Click Export list to CSV.

Export list to CSV icon.

Step 6

If prompted, save the .CSV file.

Step 7

Open the .CSV file in a spreadsheet application to sort and filter the results.


The device and service information is exported to a .CSV file that can be opened and manipulated in spreadsheet applications for sorting and filtering purposes.

Export device configuration

Export a device's configuration to a JSON file for backup, analysis, or migration purposes.

You can only export one device configuration at a time.

Procedure


Step 1

Choose Inventory.

Step 2

Choose Security Devices.

Step 3

Click the Devices tab to locate the device or the Templates tab to locate the model device.

Step 4

Click the appropriate device type tab.

You can use the filter and search functionalities to find the required device.

Step 5

Select the device you want so it is highlighted.

Step 6

In the Actions pane, select Export Configuration.

Step 7

Select Confirm to save the configuration as a JSON file.


The device configuration is exported and saved as a JSON file to your local system.

Bulk reconnect devices to Security Cloud Control Firewall Management

This task allows administrators to attempt to reconnect multiple managed devices to Security Cloud Control Firewall Management simultaneously to restore management capabilities.

Security Cloud Control Firewall Management allows an administrator to attempt to reconnect more than one managed device to Security Cloud Control Firewall Management at the same time. When a device Security Cloud Control Firewall Management manages is marked "unreachable," Security Cloud Control Firewall Management can no longer detect out of band configuration changes or manage the device. There could be many different reasons for the disconnect. Attempting to reconnect the devices is a simple first step in restoring Security Cloud Control Firewall Management's management of the device.


Note


If you are reconnecting devices having new certificates, Security Cloud Control Firewall Management automatically reviews and accepts the new certificates on the devices and continues to reconnect with them. However, if you are reconnecting with only one device, Security Cloud Control Firewall Management prompts you to review and accept the certificate manually to continue to reconnect with it.


Procedure


Step 1

In the left pane, click Security Devices.

Step 2

Click the Devices tab to locate devices.

Step 3

Click the appropriate device type tab.

Use the filter to look for devices whose connectivity status is "unreachable."

Step 4

From the filtered results, select the devices you want to attempt to reconnect.

Step 5

Click Reconnect The image illustrates a user interface displaying a filter option to identify devices with an "unreachable" connectivity status for bulk reconnection.. Notice that Security Cloud Control only provides command buttons for actions that can be applied to all the selected devices.


The selected devices are reconnected to Security Cloud Control Firewall Management, restoring management capabilities and allowing detection of configuration changes.

Moving devices between organizations

Moving devices between organizations is a process that:

  • requires removing devices from the current Security Cloud Control Firewall Management organization

  • involves re-onboarding the devices to the new organization, and

  • cannot be performed through direct migration between organizations.

Device migration requirements

After onboarding devices to a Security Cloud Control Firewall Management organization, you cannot migrate the devices from one Security Cloud Control Firewall Management organization to another. If you want to move your devices to a new organization, you need to remove the devices from the old tenant and re-onboard them to the new organization.

Device certificate expiry detection

Device certificate expiry detection is a monitoring feature that

  • actively monitors the expiration status of management certificates and Cisco Secure Client certificates

  • notifies users when these certificates are nearing their expiration date or have expired, and

  • prevents disruptions in device operations due to certificate expiry.

Certificate monitoring scope and functionality

The management certificate is used for accessing FDM-managed and ASA devices from Security Cloud Control Firewall Management, while the Cisco Secure Client (formerly AnyConnect) is necessary for using virtual private network features on ASA, FDM-managed, and FTD devices from Security Cloud Control Firewall Management.

The management certificate expiry check applies to ASA and FDM-managed devices, while the Secure Client certificate expiry check applies to ASA, FDM-managed, and FTD devices.

View certificate expiry notifications

In the top right corner, click the Notifications ( The image illustrates the Notifications icon in the top right corner of the interface, highlighting its role in displaying recent alerts related to device certificate expirations.) icon to view the most recent alerts that have occurred or affected the devices you have onboarded to your tenant. The High Priority section displays the certificate expiration notifications.

These notifications are sent 30, 14, and 7 days before the certificate expiration date and then every day thereafter until the certificate either expires or is renewed with a valid certificate. You can also subscribe to receive these notifications by email on the Notification Settings section of the user preferences page. For more information, see User Notification Preferences.

Write a device note

This task allows you to create a single, plain-text note file for a device to document important information or configuration details.

Use this procedure to create a single, plain-text, note file for a device.

Procedure


Step 1

In the left pane, click Security Devices.

Step 2

Click the Devices tab to locate the device or the Templates tab to locate the model device.

Step 3

Click the appropriate device type tab.

Step 4

Select the device or model you want to create a note for.

Step 5

In the Management pane on the right, click Notes. The device note is successfully created and saved, allowing for documentation of important information about the device for future reference..

Step 6

Click the editor button on the right and select the Default text editor, Vim, or Emacs text editors.

Step 7

Edit the Notes page.

Step 8

Click Save.

The note is saved in the tab.


The device note is successfully created and saved, allowing you to document important information about the device for future reference.

Delete a device from Security Cloud Control Firewall Management

This task removes a device from your security management platform to free up licensing or decommission unused devices.

Use this procedure when you need to permanently remove a device from your security infrastructure management. The device will no longer be monitored or managed after deletion.

Procedure


Step 1

Choose Security Devices.

Step 2

Select the device you want to delete.

Step 3

Click Remove in the Device Actions pane.

Step 4

To confirm device removal, click OK.

To keep the device onboarded, click Cancel.

Note


Both devices in an FDM-managed high-availability (HA) pair must be deleted simultaneously. Click the FDM-managed HA pair name instead of selecting individual peers.


The device is permanently removed from Security Cloud Control Firewall Management and is no longer managed or monitored by the platform.

Back up Firewall Threat Defense devices

Back up Firewall Threat Defense devices to ensure configuration data can be restored if needed.

Different backup procedures apply depending on how your Firewall Threat Defense devices are managed - through Cloud-Delivered Firewall Management Center, on-premises On-Premises Firewall Management Center, or Firewall Device Managers.

Procedure


Step 1

For Firewall Threat Defense devices managed by Cloud-Delivered Firewall Management Center, access the management interface.

Step 2

For Firewall Threat Defense devices managed by On-Premises Firewall Management Center onboarded to Security Cloud Control Firewall Management, access the management center.

  • In the Security Cloud Control left pane, choose Administration > Firewall Management Center.

  • Choose the On-Premises Firewall Management Center whose Firewall Threat Defense devices you want to back up.

  • Click FMC Cross Launch URL on the right pane to navigate to the On-Premises Firewall Management Center or manually log in to the On-Premises Firewall Management Center.

  • Continue to follow the steps in Back up a Device from the Management Center in the Cisco Secure Firewall Management Center Administration Guide.

Step 3

For Firewall Threat Defense devices managed by Firewall Device Managers onboarded to Security Cloud Control Firewall Management, use the FDM backup procedure.

Follow the steps in Back up an FDM-managed Device.


Device configuration backups are created and available for restoration when needed. The backup location depends on the management type used for your devices.

Manage Firewall Threat Defense devices through Security Cloud Control Firewall Management

Security Cloud Control Firewall Management provides a unified interface to manage Firewall Threat Defense devices, both in hardware and virtual formats.

Firewall Threat Defense devices associated with these three management applications can be managed on the Security Cloud Control platform:

  • Secure Firewall Device Manager

  • Secure Firewall Management Center

  • Secure Cloud-Delivered Firewall Management Center

Procedure


Step 1

Log in to the Security Cloud Control platform.

Step 2

In the left pane, click Security Devices.

Step 3

Click the FTD tab.

Step 4

Click The filter pane under Devices/Services allows users to display devices based on the management application used for access. at the top-left corner.

Under Devices/Services, the filter pane provides filters that display Firewall Threat Defense devices based on the management application through which they are accessed from Security Cloud Control.

  • FDM: Firewall Threat Defense device managed by Firewall Device Manager

  • FMC-FTD: Firewall Threat Defense devices managed by Firewall Management Center

  • FTD: Firewall Threat Defense devices managed by Cloud-Delivered Firewall Management Center

Step 5

To view the Firewall Threat Defense devices under a management application, check the corresponding check box.


The Firewall Threat Defense devices associated with the selected management application are displayed.

Filter security devices by hardware end-of-life status

Use the Hardware End-of-Life filter to identify devices that are approaching or have reached their hardware end-of-life date for support planning and risk mitigation. This helps ensure you maintain supported hardware configurations and avoid operational and security risks associated with unsupported devices.

Running unsupported hardware may pose operational and security risks because Cisco no longer provides software updates, security patches, or technical support after the EoL date.


Note


The Hardware EoL filter currently supports Firewall Threat Defense devices managed by On-Premises Firewall Management Center and Cloud-Delivered Firewall Management Center, and ASA devices.


Procedure


Step 1

In the Devices tab, click the filter icon.

Step 2

From the list of available filters, under Device End-of-Life, select Hardware End-of-Life.

The list now displays all devices that are approaching or have reached their hardware end-of-life.

Step 3

Select a device to view more information on the right pane.

Step 4

Scroll down to the Device End of Life section to view the following details:

  • The exact end-of-life date.

  • Remaining time until the last day of support.

Step 5

Click Know more.

You can view a detailed page that provides the following information:

  • Cisco's recommended replacement devices with product specifications, along with links to view the official data sheets.

  • Guidance on submitting a request through the Contact Cisco page and options to connect directly with Cisco experts.

  • Information on Cisco's product recycling program.

Step 6

Click Export to download the device report in CSV format for offline analysis.


You have successfully filtered devices by hardware end-of-life status and can now view devices that require attention for support planning. You can also access detailed replacement information and export device reports for further analysis.

Security Cloud Control Firewall Management labels and filtering

A label is a grouping mechanism that

  • groups devices or objects for organizational purposes

  • can be applied to one or more devices during onboarding or any time after onboarding

  • enables filtering of device table or objects table contents using the corresponding label, and

  • allows creation of label groups using the syntax group name:label.

Label application and filtering information

You can apply labels to objects after creating them. Once you apply labels to devices and objects, you can filter the contents of the device table or objects table using the corresponding label.


Note


A label that is applied to a device is not extended to its associated objects, and a label applied to a shared object is not extended to its associated objects.


You can create a label group by using the syntax group name:label, for example, Region:East or Region:West. If you create these two labels, the group label would be Region and you could choose from East or West in that group.

Apply labels to devices and objects

Applying labels helps organize and categorize devices and objects for easier identification and management within the system.

Labels provide a way to group and identify devices and objects based on their function, location, or other relevant criteria. You can apply labels to both devices in the inventory and objects in the objects management interface.

Procedure


Step 1

To add a label to a device, click Inventory in the navigation pane on the left.

Step 2

In the left pane, click Security Devices.

Step 3

To add a label to an object, click Objects in the navigation pane on the left.

Step 4

In the left pane, click Objects.

Step 5

Click the Devices tab to locate a device or the Templates tab to locate the model device.

Step 6

Click the appropriate device type tab.

Step 7

Select one or more devices.

Step 8

In the Add Groups and Labels field on the right, specify a label for the devices.

Step 9

Click the The label is applied to selected devices and objects for filtering and organizing items in the interface. icon.


The label is applied to the selected devices or objects and can be used for filtering and organizing items in the interface.

Filters on security devices, policies, and objects page

Filters on security devices, policies, and objects page are navigation tools that

  • help you find specific devices and objects by filtering based on various criteria

  • allow filtering by attributes such as device type, hardware version, software version, Snort version, configuration status, connection state, conflict detection, Secure Device Connector, and labels, and

  • are accessible through the filter icon in the left pane of the Security Devices, Policies, and Objects pages.

Filter functionality by device type

On the Security Devices page, the filter panel lets you filter devices by criteria such as device type, hardware version, software version, Snort version, configuration status, connection state, conflict detection, Secure Device Connector, and labels. You can apply filters within the selected device type tab.

When the FTD tab is open, the filter panel also lets you filter FTD devices by the management application that Security Cloud Control uses to access them.

To filter, click The filter panel on the Security Devices page allows users to filter devices by various criteria, including device type, hardware version, and connection state. in the left-hand pane of the Security Devices, Policies, and Objects tabs.


Note


When the FTD tab is opened, the filter pane provides filters to show FDM-managed devices based on the management application through which the devices are accessed from Security Cloud Control.

  • FDM: Devices managed using FTD API or Firewall Device Manager.

  • FMC-FTD: Devices managed using Firepower Management Center.

  • FTD: Devices managed using FTD Management.


Use Security Cloud Control Firewall Management search functionality

The Security Cloud Control Firewall Management search functionality is a platform feature that

  • provides a highly efficient search function that makes it easy to find anything you need,

  • includes a search bar on each page that is tailored to the content of that page, and

  • offers global search that allows for a comprehensive search across the entire tenant.

Search functionality benefits

This search functionality saves time and effort, as you can quickly locate the necessary information.

Global search

A global search is a centralized search functionality that

  • allows you to search for onboarded devices and associated objects available within Security Cloud Control

  • enables you to navigate to device and object pages directly from search results, and

  • provides quick location and navigation to devices managed by Security Cloud Control.

Global search indexing options and supported entities

  • Full Indexing—Requires that you invoke the full indexing process. This process scans all the devices and objects in the system and displays them in the search index only after you invoke the indexing. To invoke full indexing, you must have administrative privileges.

    For more information, see Initiate full indexing.

  • Incremental Indexing—An event-based indexing process where the search index automatically updates each time that a device or an object is added, modified, or deleted.

The information that you enter in the search field is not case-sensitive. You can perform a global search using these entities:

  • Device Name—Supports partial device names, URL, IP address, or range.

  • Object Types—Supports object name, object descriptions, and configured values.

  • Policy Types—Supports policy name, policy description, rule name, and rule comments.

    Cloud-Delivered Firewall Management Center and on-premises Firewall Management Center managed in Security Cloud Control support these policy types:

    • Access Control Policy

    • Prefilter Policy

    • Threat Defense NAT Policy

When you type a search expression, the interface begins to display search results and you do not need to press Enter to execute a search.

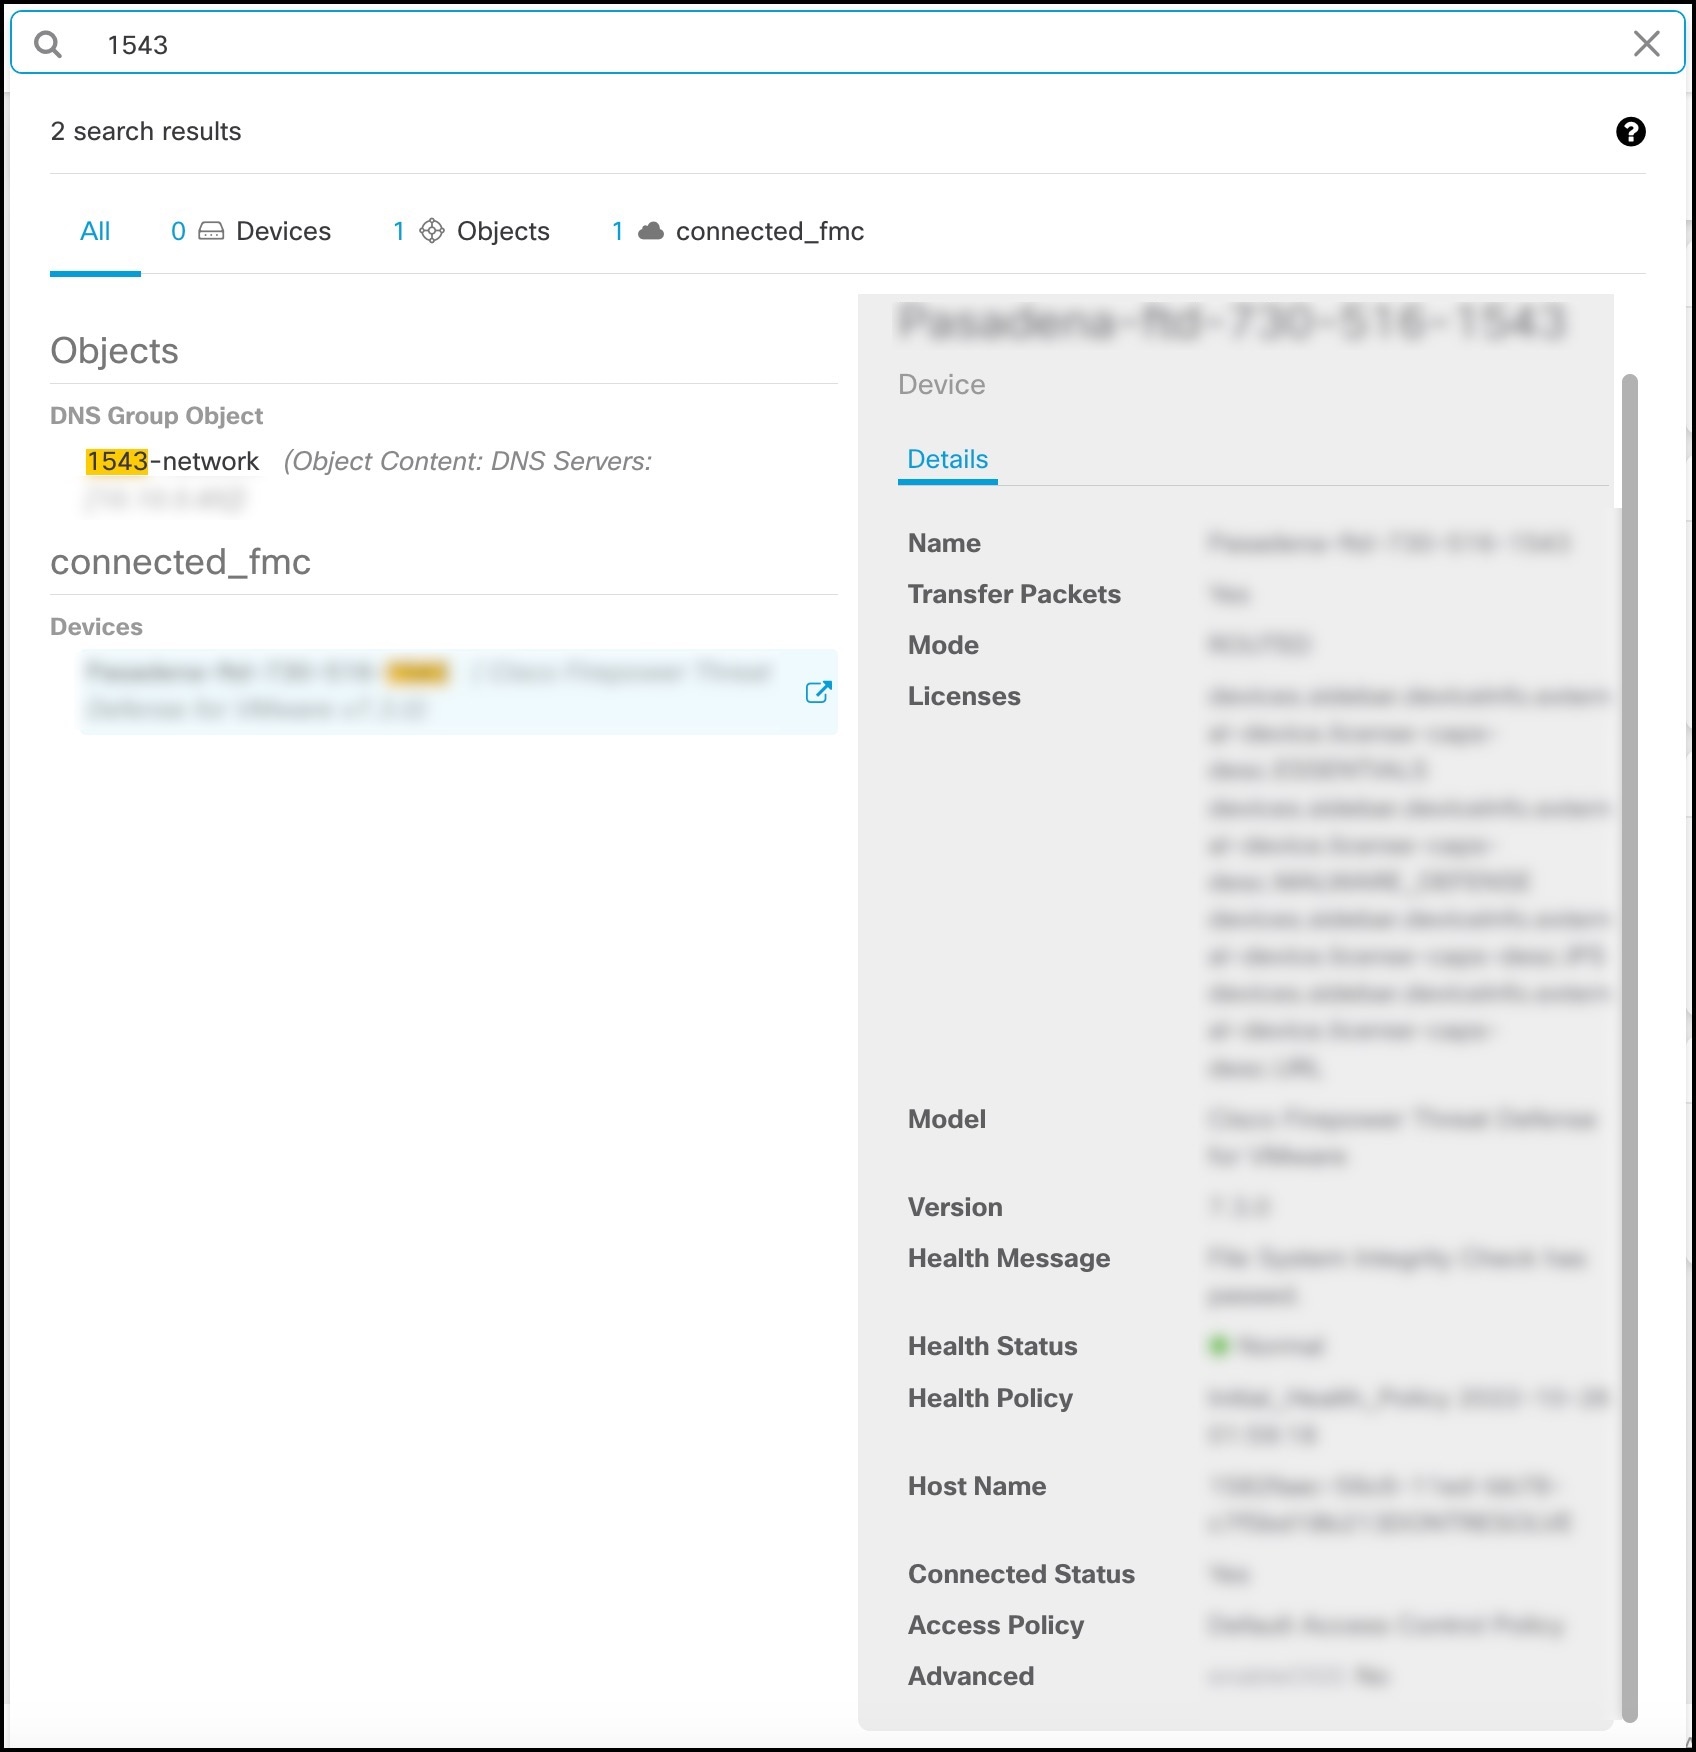
The search results display all devices and objects that match your search terms. If your search term matches more than one device or object, the results appear under categories such as devices, objects, and connected_fmc.

By default, the first item in the search result is highlighted and the related information for that item appears in the right pane. You can scroll through the search results and click any item to view the corresponding information. You can click the arrow icon besides the item to navigate to the corresponding page.


Note


  • Global search does not display duplicate search results. For objects, the unique identifier of the shared object is used to navigate to the Object view.

  • If you delete a device from Security Cloud Control, all associated objects are removed from the global search index.

  • If you delete an object from the policy and retain the device before you initiate full indexing, the object remains in the global search index because it is associated with the device.


Initiate full indexing

Initiate full indexing to enable global search capabilities for your tenant.

Procedure

Step 1

In the left pane, choose Administration > General Settings.

Step 2

In the left pane, click Administration > General Settings.

Step 3

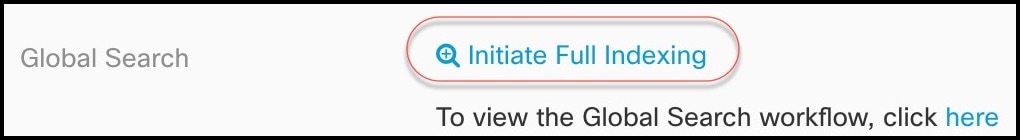
In Global Search, click Initiate Full Indexing to trigger indexing.

The diagram illustrates the process of initiating full indexing, highlighting the steps involved in clearing existing indexing for the tenant.

Note


Initiating full indexing clears existing indexing of the Security Cloud Control tenant.


Step 4

Click here to view the global search workflow.


Full indexing is initiated and global search functionality becomes available for your tenant.

Perform a global search

Use global search to quickly locate and navigate to specific devices, objects, policies, and Cloud-Delivered Firewall Management Center items across your environment.

Procedure

Step 1

Log into Security Cloud Control.

Step 2

Click the search icon in the Security Cloud Control page and enter the search strings in the search field that appears.

Alternatively, you can press and hold the Ctrl key and the / key simultaneously on Windows, or the Command key and / key on Mac, to open the search bar.

The search bar interface shows the categories for search results, including All, Devices, Objects, and Policies, along with a preview of the selected item in the right pane.

The search results display a list of possible items as you begin entering the search strings. The search results appear under four categories: All, Devices, Objects, Policies, and Cloud-Delivered Firewall Management Center. The right pane displays information for a selected search result.

The search results interface shows a categorized list of items based on entered search strings, with details displayed for the selected result in the right pane.

Step 3

From the search result, select a device or an object, and click the arrow icon to navigate from the search results to the corresponding device and object page. From the search result, select an item, and click the arrow icon to navigate from the search results to the corresponding page.


Note


Selecting a search result for devices in the Cloud-Delivered Firewall Management Center, allows you to navigate to the Cloud-Delivered Firewall Management Center user interface within Security Cloud Control.

For information on Cloud-Delivered Firewall Management Center, see Managing Firewall Threat Defense with Cloud-Delivered Firewall Management Center in Security Cloud Control.


Step 4

Click X to close the search bar.


You have successfully performed a global search and navigated to the desired device, object, or policy page. The search bar is now closed.