Agentic security refers to the application of autonomous AI agents—software entities capable of making decisions and taking actions without constant human oversight—to the field of cybersecurity.
Your workforce now includes AI agents. Secure it accordingly.
See every agent, govern every action, and contain every risk.
Most identity tools see only what logs in. Cisco sees identity and network together, so shadow agents surface the moment they act.
Agents chain requests across models, tools, and APIs. Cisco SASE authorizes each one just in time, without exposing credentials to the agent.
Agents move across clouds, data centers, and branches. Cisco Hybrid Mesh Firewall carries policy with them, so one rogue agent can't become a breach.
Agents move at machine speed
See how to protect your organization
Distributed security fabric
As attackers weaponize AI, traditional security approaches fall short. Contain threats at every hop and protect applications where they live.
Security and networking as one
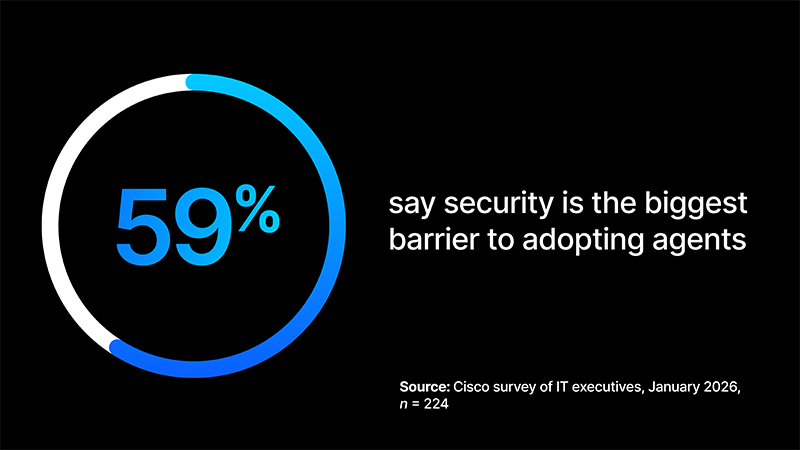
Most organizations can't yet control what their agents do. Govern agent actions with guardrails and live monitoring, not just access.
Comprehensive AI security
When agents move at machine speed, fewer than one in three organizations can detect or prevent AI-specific threats. Block unsafe agent actions and protect product AI with guardrails in the network.
Connected by one network. Protected by one platform.
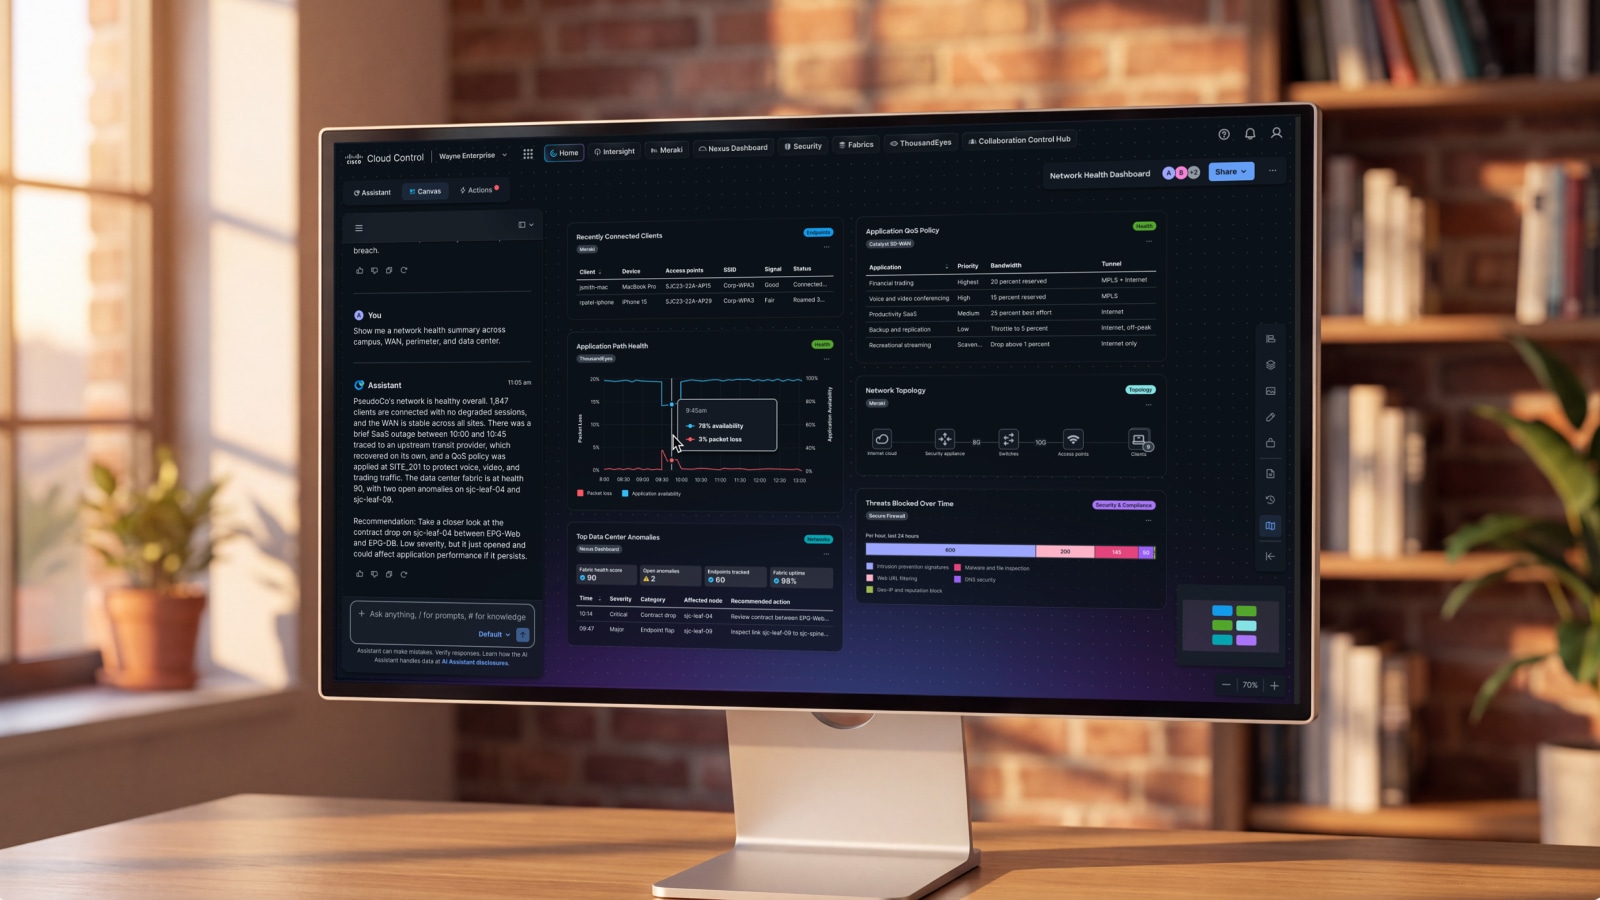
Agents, users, and apps run across your edge, WAN, and every cloud. Cisco Cloud Control gives teams shared policy and context to keep work moving securely.
1
Stop advanced threats
Stop zero-day threats with distributed security fabric leveraging Snort ML and Talos Threat intelligence, powered by Cisco Firewall.
2
Secure agents in every cloud
Extend Layer-7 firewalling capabilities to the cloud, natively with Cisco Multicloud Defense.
3
Keep agent work moving
See exactly where work slows or fails with Cisco ThousandEyes while Cisco SASE steers AI and agent traffic by path health.
4
Know and authorize every agent
Map each agent to an owner with Cisco Duo and Identity Intelligence while Agent Gateway grants just-in-time access.
5
Protect the foundation
Keep edge and WAN infrastructure trusted during attacks and changes with Cisco Live Protect and quantum-safe protection.
6
Identify and protect agents
Discover AI workloads, users, and apps across clouds, mitigate real-time threats, protect against data leaks, and identify vulnerabilities across models at scale with Cisco AI Defense.
Explore agentic security resources

Close the agent trust gap

Secure agent access anywhere

Apply zero trust to agentic AI

Enforce consistent policy everywhere
Frequently asked questions about agentic security
An agentic swarm is a collaborative architecture where multiple autonomous agents communicate and coordinate with one another to solve complex security challenges that would be difficult for a single agent to handle in isolation. In a security environment, these agents act as a collective force, sharing intelligence and distributing tasks across the infrastructure to harden defenses.
Hybrid mesh firewall is a distributed security architecture that moves firewall functionality away from a traditional perimeter bottleneck and directly into the fabric of the network, including the data center, cloud, and edge. Powered by Cisco Hypershield, this approach uses a software-defined mesh to place security enforcement points precisely where they are needed, such as in front of individual workloads.
Secure access service edge (SASE) is a modern architectural framework that converges wide-area networking (WAN) capabilities with comprehensive cloud-native security functions.
Secure access and hybrid mesh firewall serve as critical components within the broader SASE framework, providing the necessary protection for modern, distributed environments. Secure access provides the identity-based, zero-trust connection for users and devices, while the hybrid mesh firewall provides the deep-packet inspection and workload-level protection for the infrastructure itself. Together, they bridge the gap between user connectivity and data protection, ensuring that the SASE architecture is not only managing traffic flow but is also actively enforcing security policies across both the user edge and the data center core.
Cisco Cloud Control is essential for organizations seeking centralized visibility and policy orchestration across a distributed, multicloud environment. If your organization operates a complex hybrid setup—utilizing both on-premises data centers and various public clouds—Cloud Control acts as the single platfrom required to manage your agentic security policies, firewall rules, and compliance mandates.
Protecting the edge and WAN requires a transition toward a SASE-driven architecture, augmented by the proactive capabilities of a hybrid mesh firewall.
Determining your specific security requirements starts with an assessment of your current infrastructure, your regulatory compliance needs, and your risk profile.
This page includes imagery created with the assistance of AI.
Source: AI Impact on Wide Area Networks: Cisco Report 2026